Support for the Security Rule Base
After global properties are configured, the firewall administrator configures specific rules, or packet filters, that determine how certain incoming or outgoing packets are handled. During import from NetCollector, one entry for each explicit rule is created in the FireWall-1 security rule base.
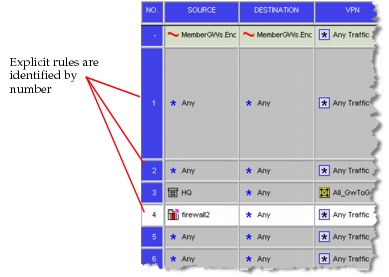
Rules in FireWall-1 are identified by a number, as shown in Figure 107. When the FireWall-1 configuration is imported to NetCollector, the rule numbering remains intact. These rules retain the mapping when imported from NetCollector into NetPlanner.
Figure 107: Rule Numbering in FireWall-1
The rules from the FireWall-1 security rule base are mapped to two locations:
- Rule parameters including source, destination, action, and so on, map to specific rows in Security > Firewall Parameters > Access List Configuration > Access List Definitions.
- The direction to which the rule should be applied maps to specific rows in the Security > Firewall Parameters > Packet Filters compound attribute.
Rule Parameters
Import maps a given rule, identified by row number in the FireWall-1 security rule base, to a compound attribute in NetPlanner, using “rule-n” to correlate the entry with the row number from the security rule base. Figure 108 also shows a packet filter entry for an access list imported from the Nokia IPxxx firewall appliance. This is discussed further in Nokia Appliance Platform Support.
Figure 108: FireWall-1 Rule in Rule Base and in NetPlanner
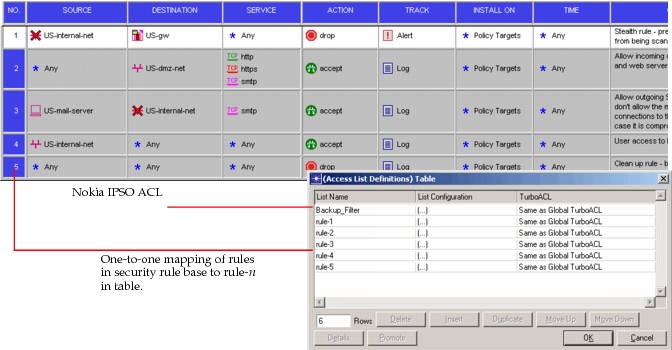
Note: TurboACL is not applicable to Check Point FireWall-1 configurations.
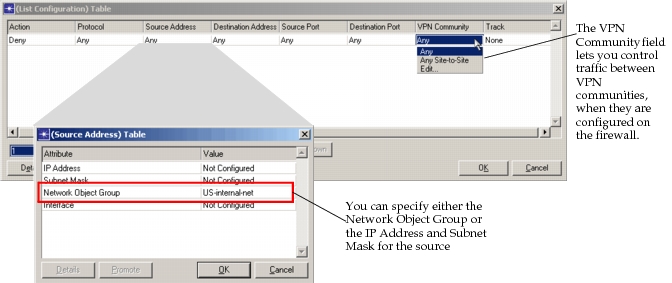
Specific rule parameters map to the List Definition compound attribute in the table depicted in Figure 108. For each rule row, the action, protocol, source/destination address and port, and tracking method are mapped, as shown in the following figure.
Figure 109: List Definitions Table
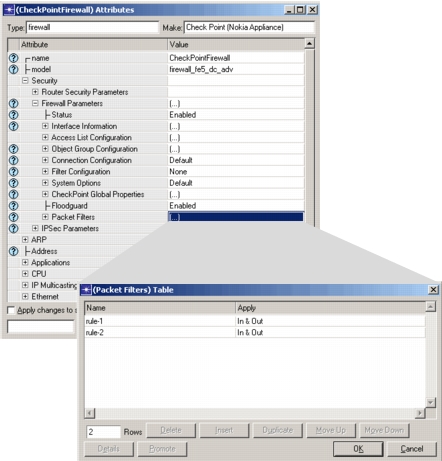
The direction to which the rule is applied is defined in the Security > Firewall Parameters > Packet Filters table, shown in Figure 110. Each row in the FireWall-1 security rule base maps to a corresponding “rule-n” in the Packet Filters table.
Figure 110: Firewall Parameters in NetPlanner
Rules are applied as follows:
- In – Applied to traffic destined to the firewall.
- Out – Applied to traffic originating from the firewall.
- In&Out – Applied to traffic traversing the firewall.