Importing Check Point FireWall-1: Introduction
Check Point FireWall-1 is a software-based security product that can be installed on Windows, Linux, and Solaris platforms and is alternately available pre-integrated into a Nokia IP xxx appliance. You can import the configuration of Check Point FireWall-1 into NetCollector by using the CheckPoint Rule&Object File Import adapter. (For more information about the adapter, see the Adapters chapter of NetCollector User Guide). You can then import the configuration of the firewall into NetPlanner from NetCollector.
This section describes the support provided for Check Point FireWall-1 and how to import and leverage the configuration. In configuring FireWall-1, the administrator sets global properties and specific policies. In addition to certain global properties, the following components of FireWall-1 are supported:
- Security Rule Base
- Address Translation Rule Base
- VPN
In FireWall-1, a Security Rule Base comprises device-centric packet filters, multiple filters applied to data traffic, and implicit rules. The Address Translation Rule Base support includes device-centric network address translation (NAT) and both server-side and client-side NAT. Virtual Private Networks (VPN) permit secure communication between gateways (firewalls).
Figure 95: Supported Elements in FireWall-1 Configuration
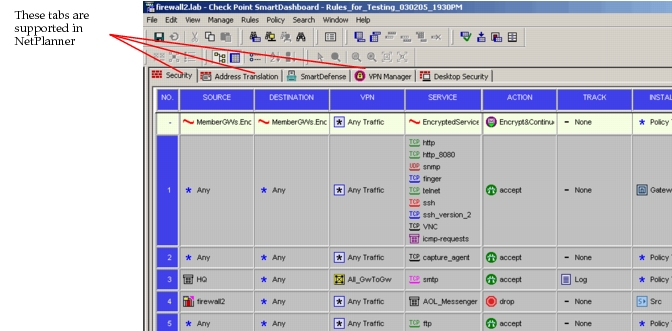
Specifically, support is provided for the following configuration elements, each of which is described further in the sections that follow:
- FireWall-1
- Global Properties Support for FireWall-1 – Implied Rules, Stateful Inspection, NAT, and Log and Alert.
- Support for the Security Rule Base
- Anti-Spoof Check
- Address Translation Rule Base
- VPN-1
- Security Rule Base
- VPN-1 Net