Anti-Spoof Check
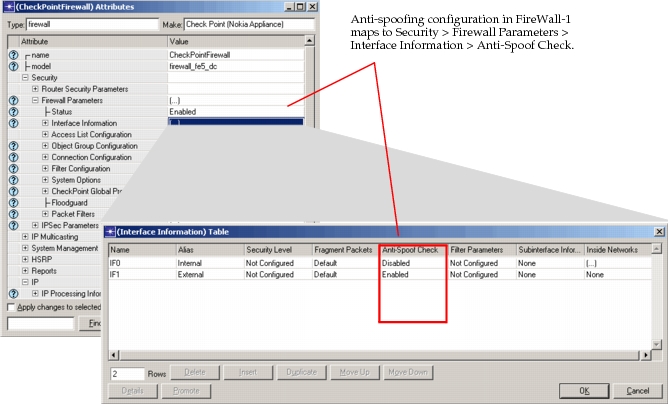
Checking for spoofed addresses is an important part of an overall network security policy. Anti-spoofing rules, as defined in FireWall-1, are modeled on a per-interface basis in NetPlanner. In the Check Point FireWall-1 software, anti-spoofing is configured on an interface of the firewall object to check the source IP address of incoming packets. The following figure shows an example of this configuration.
Figure 111: Anti-Spoof Configuration on FireWall-1
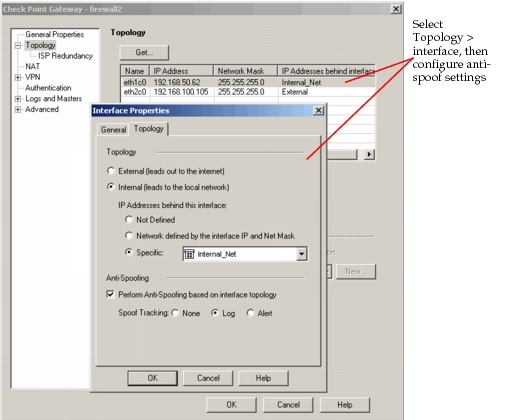
After import, the anti-spoofing configuration maps to the interface configuration on the firewall object in the network model. The following figure shows how the information is mapped.
Figure 112: Anti-Spoof Configuration in NetPlanner