Importing Juniper SRX Firewall: Introduction
Juniper SRX firewall is an integrated network security solution that comprises a network appliance bundled with the JUNOS operating system. You can import the configuration of Juniper SRX firewalls from NetCollector or from JUNOS configuration files using eXpress Data Import.
System Requirements for Import of Juniper SRX Firewall
To import Juniper SRX firewalls, you need the following products:
- NetPlanner with eXpress Data Import
- (optional) NetCollector
Security Zones in the Juniper SRX Firewall
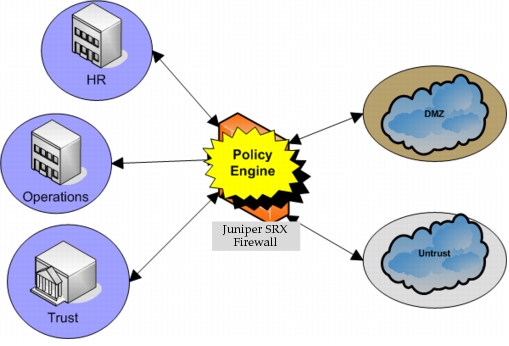
This section discusses security zones. A security zone is a logical entity to which one or more interfaces are bound. The SRX firewall configuration includes three default security zones: Trust, Untrust, and DMZ (Layer-3), or V1-Trust, V1-Untrust, and V1-DMZ (for Layer-2). You can use these default security zones in addition to user-defined zones. Figure 147 shows the three default zones configured plus two user-defined zones: HR and Operations. Once the security zones are configured, the SRX firewall administrator can add interfaces to the zones and configure policies that regulate traffic between and within the zones. The policy engine on the SRX firewall contains this regulatory information.
Note: Network Address Translation (NAT) and transparent modes for interfaces are not currently supported. Only interfaces in routed mode are supported.
Figure 147: Example of Security Zones in a Network
Note: Each security zone can have one or more interfaces bound to it, a concept shown more specifically in Figure 149.
Security zones are imported into the model attributes as shown in Figure 148.
Figure 148: Security Zones Attributes
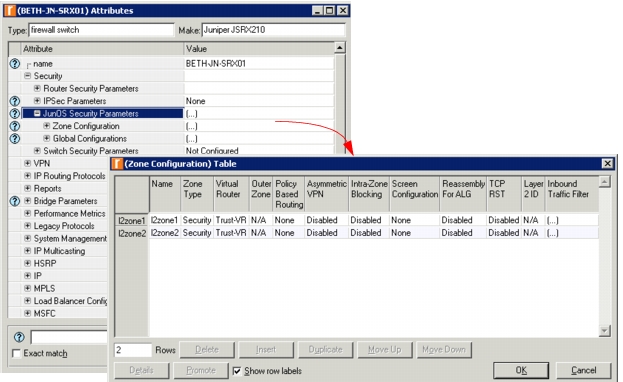
Note: Only security zones, no tunnel zones, are currently supported.
Virtual Routers in the Juniper SRX Firewall
Juniper SRX firewall also uses the concept of a virtual router. A virtual router (VR) functions as a router, having its own interfaces and its own unicast and multicast routing tables. Two predefined VRs exist on the firewall: trust-vr and untrust-vr. Even though both VRs are already defined, you must either export routes between the VRs or create a static route between them, if you want to pass traffic between the VRs during an analysis.
Note: Multicast routing is not supported for this release.
The network example shown in Figure 149 has security zones assigned to the predefined virtual routers. Both predefined and user-defined security zones are in use, with one interface per security zone. This is a simple network example; each security zone could have multiple interfaces assigned. An interface allows traffic to pass into and out of the security zone with which it is associated, while security policies dictate how traffic flows between interfaces.
Figure 149: Example of Virtual Router Configuration
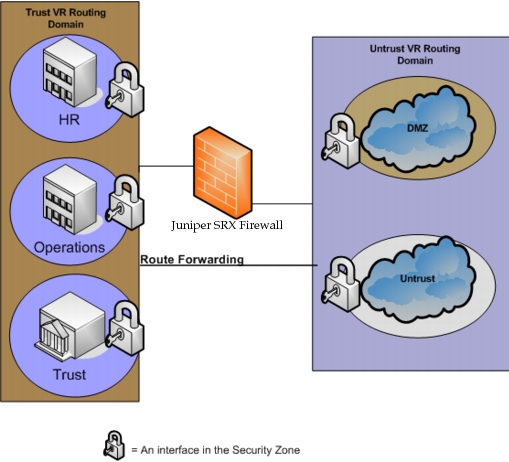
Virtual routers configurations are imported into the IP > IP Routing Parameters attributes.
Virtual Private Networks
The Juniper SRX firewall supports several types of virtual private networks (VPN) between sources and destinations in the network. The following types of VPNs are supported for analysis in NetPlanner:
-
Policy-Based VPN
A policy-based VPN is an SRX configuration in which a VPN is referenced in the security policy with an Action of “tunnel.”
-
Route-Based VPN
A route-based VPN is an SRX configuration that, unlike the policy-based VPN, does not have a rule that references a VPN tunnel. Traffic is routed to a tunnel interface that in turn references a tunnel. Components of a route-based VPN include
- A tunnel, consisting of a tunnel name, tunnel source/destination, and encapsulation
- One or more tunnel interfaces bound to a security zone
- A one-to-one or one-to-many relationship between a tunnel interface and tunnel(s). In a one-to-many relationship, the interface is bound to multiple VPNs using Next Hop Tunnel Binding (NHTB) with a destination of a tunnel.
- Action is “Permit” or “Deny”
SRX Clusters
When you import a network model containing Juniper SRX firewall clusters, the import process examines the configuration data and models one or two nodes in the topology, based on the information gathered from NetCollector. Interfaces associated with the cluster in NetCollector are associated with their native Juniper SRX firewall in the resulting topology. You can perform a flow analysis or failure analysis, and run capacity planning on network models containing Juniper SRX clusters.
The following attribute contains the Juniper SRX cluster configuration:
- System Management > Redundancy Parameters > Chassis Cluster Parameters
During a flow analysis, NetPlanner uses node priority and group configuration to determine how the flow will traverse the SRX devices in a cluster. Tracking parameters for each group (per interface) change the priority for a group if an interface fails.